
gustavofreze/php
Hardened, reproducible PHP base images: runtime, development, builder and cli. Non-root.
100K+
gustavofreze/php repository overview
gustavofreze/php
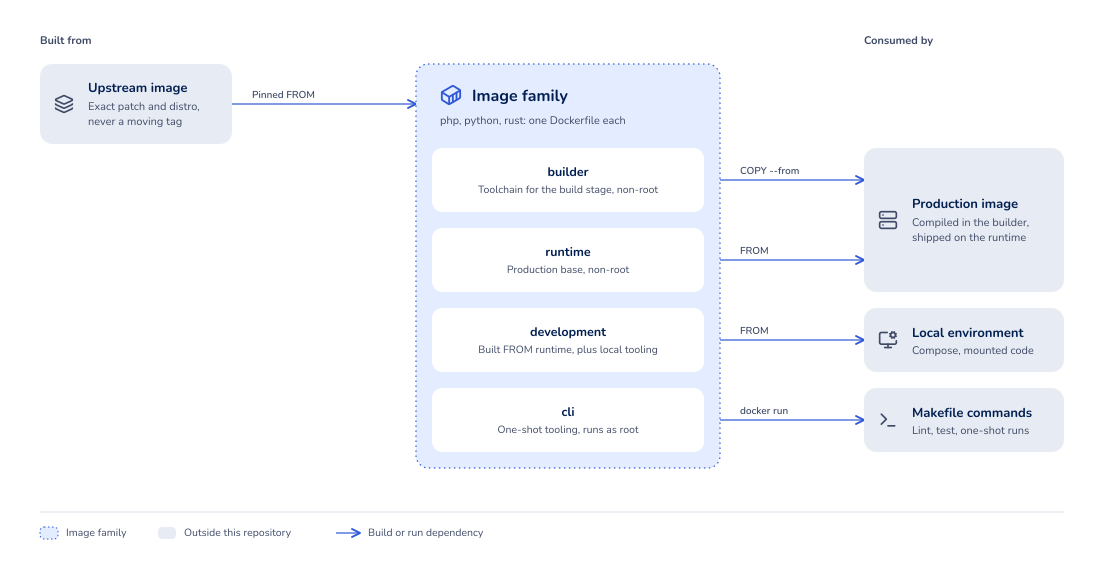
Hardened, reproducible PHP base images. One Dockerfile per upstream version ships four targets: the production runtime
(PHP-FPM), its development variant, the builder for a project's production build, and a cli tooling image a
project Makefile invokes.
Quick reference
- Maintained by: Gustavo Freze
- Source: gustavofreze/docker-images
- File an issue: docker-images/issues
- Also published as:
ghcr.io/gustavofreze/php - Architectures:
linux/amd64,linux/arm64 - Supply chain: every tag ships a build provenance attestation and an SBOM, and carries no accepted risk
- License: MIT
Supported tags
| Tag | Alias | Purpose |
|---|---|---|
8.5-runtime-1.0.11 | 8.5-runtime | Production PHP-FPM runtime. |
8.5-development-1.0.11 | 8.5-development | Local development: runtime plus Xdebug, Composer, bash, git. |
8.5-builder-1.0.11 | 8.5-builder | Composer toolchain for the builder stage of a production image. |
8.5-cli-1.0.11 | 8.5-cli | Makefile tooling: Composer, Xdebug coverage, linters, docker. |
Every tag is <upstream-minor>-<target>-<version>. There is no bare tag and latest is forbidden.
- Versioned tag. Immutable and reproducible. It moves only when you bump it, so take it for anything that ships.
- Alias. Tracks the latest rebuild of its target, the monthly security rebuild included, and never crosses an
upstream minor:
8.5-runtimestays on 8.5. It moves only when the client re-pulls, which suitscliand local development.
All four are built from one multi-target
Dockerfile, pinned to
php:8.5.12-fpm-alpine3.24. Every tool it adds is pinned there too.
Image variants
| Target | Runs as | Health check | On top of the base |
|---|---|---|---|
runtime | www-data (uid 82) | FPM socket | Extensions, production hardening, production OPcache. |
development | www-data (uid 82) | FPM socket | runtime plus Xdebug 3, Composer 2, bash, git, development OPcache. |
builder | www-data (uid 82) | none | Composer 2, git, unzip. |
cli | root | none | builder plus Xdebug coverage, bash, curl, linters, the docker CLI. |
developmentis builtFROM runtime. It runs on a developer machine and is never deployed.builderis discarded in the multi-stage application build. It installs dependencies non-root, so the vendor tree it produces already carries the runtime's ownership.clistays root so it can write into a bind mount owned by the caller.- Every target is built on the FPM base, so the family shares one base layer.
builderandcliinherit itsEXPOSE 9000as metadata only: nothing in either image listens, and their default command is the interactive PHP shell.
What it provides
Every image provides, and no consuming Dockerfile re-declares:
- Extensions. The official image set (curl, sodium, mbstring, and the rest) plus
bcmath,pdo_mysql, andzip, built with no leftover build dependencies. - A non-root runtime. PHP-FPM runs as
www-data, withWORKDIR /var/www/htmlowned by it. - Current system libraries. openssl, curl, brotli, and zlib are upgraded to what the Alpine index serves at build time, instead of aging in place between base releases.
- Production hardening.
php.ini-productionactive,expose_php,display_errors, andallow_url_includeoff, arguments stripped from exception traces, strict and transport-locked session cookies, session upload progress disabled, and the process escape functions (exec,shell_exec,system,proc_open,popen,passthru) disabled. A project that legitimately shells out re-enables what it needs in its own drop-in. - OPcache defaults. Production tuning in
runtime(no timestamp validation, tracing JIT), development tuning indevelopment(timestamp validation on, JIT off). - A health check probing the PHP-FPM socket.
- Graceful shutdown. The official
STOPSIGNAL SIGQUITand exec-formphp-fpmcommand are preserved, andprocess_control_timeoutis 10s, so the master drains in-flight requests inside the default stop timeout ofdocker stopand Compose.
development also prints undecorated worker output in docker logs and re-enables the process functions, so Composer
can run.
The cli image is built to be piped and scripted:
- Linters. CodeSniffer as
phpcsandphpcbf, Mess Detector asphpmd, each fetched over TLS and verified against its published sha256 before it enters a layer. - Parseable output. Diagnostics go to
stderr, neverstdout, so a--report=jsonrun is parseable.phpmdis a wrapper that silences the deprecation notices Mess Detector raises on PHP 8.5, so its report is the only thing on either stream. - The docker CLI. An integration suite that drives throwaway containers can shell out to
dockeragainst a mounted host socket. No other image in this repository carries it. Mounting the socket is root-equivalent on the host, so grant it only to a local tooling invocation you control.
How to use this image
As a base image
A project consumes the base in two thin files and adds only its own dependencies, code, and tuning:
# syntax=docker/dockerfile:1
FROM gustavofreze/php:8.5-development-1.0.11
COPY ./ /var/www/html
# syntax=docker/dockerfile:1
FROM gustavofreze/php:8.5-builder-1.0.11 AS builder
COPY composer.json composer.lock ./
RUN composer install --no-dev --no-interaction --prefer-dist --optimize-autoloader
COPY ./ ./
RUN composer dump-autoload --optimize --classmap-authoritative

FROM gustavofreze/php:8.5-runtime-1.0.11
COPY --from=builder --chown=www-data:www-data /var/www/html /var/www/html
As a tooling image
The cli image is invoked directly and never appears in a Dockerfile.
To install the project dependencies, run:
docker run --rm -v "$(pwd)":/var/www/html gustavofreze/php:8.5-cli-1.0.11 composer install
To check the code style, run:
docker run --rm -v "$(pwd)":/var/www/html gustavofreze/php:8.5-cli-1.0.11 phpcs src/
As an FPM service
services:
    php:
        image: gustavofreze/php:8.5-development-1.0.11
        volumes:
            - ./:/var/www/html
        expose:
            - "9000"

    nginx:
        image: nginx:alpine
        ports:
            - "80:80"
        volumes:
            - ./public:/var/www/html/public
            - ./nginx.conf:/etc/nginx/conf.d/default.conf
        depends_on:
            - php
The rules that hold across every family live in the usage contract.
Verification
No tag is published before it passes the full
gate, on a native linux/amd64 runner and a native
linux/arm64 one:
| Stage | Tool | What it checks |
|---|---|---|
| Lint | hadolint, ShellCheck | Every Dockerfile and every RUN body. |
| Scan | Trivy and Grype | Fixable HIGH and CRITICAL vulnerabilities. |
| Audit | Dockle | The CIS Docker Benchmark. |
| Efficiency | dive | Wasted layer space. |
| Smoke | throwaway containers | The runtime contract, in throwaway containers. |
The smoke suite asserts the non-root user, the extensions, the hardening, the OPcache mode, the health check, the pinned tool versions, and the absence of development tooling in the production surface.
This family carries no accepted risk, so it publishes no OpenVEX analysis and no scanner exemption of any kind. Every scan in the gate runs bare, and what it reports is what the images contain.
To scan a tag yourself, run:
trivy image gustavofreze/php:8.5-cli-1.0.11
License
Tag summary
Content type
Image
Digest
sha256:9d719dfbe…
Size
46.6 MB
Last updated
3 days ago
docker pull gustavofreze/php:8.5-development